Zhanybek Mamataliev
Senior DevOps Engineer | DevSecOps & SRE · Brownsville, TX.
Portfolio overview and full text alternative to the interactive workspace.
About me
I build the guardrails that let thousands of engineers, and now AI agents, ship to production safely.
Senior DevOps Engineer, 14+ years across AWS, Azure, GCP, and Kubernetes. I set the technical direction for the shared DevSecOps and SRE platform behind 500+ engineering teams and 6,300+ developers: governed package and model intake, a gated delivery path, and the reliability controls behind both.
Three bets define the current work. Supply chain: every Hugging Face, npm, Maven, and PyPI dependency enters through one governed proxy, with SBOMs, Firewall ingest rules, and fixes that arrive as pull requests. Delivery: one gated template instead of a pipeline per team, now carrying 50+ microservices at 40% shorter lead time. Resilience: the artifact platform behind 7,000+ applications moved to AWS with zero downtime, and its storage spend dropped 98%.
Selected outcomes
- Zero downtime moving the build dependency of 7,000+ applications to AWS, with 99.99% availability held
- 98% lower artifact-storage spend through automated S3 versioning and lifecycle tiering
- One gated delivery path across 50+ microservices; 40% shorter deployment lead time
- 20+ applications moved off on-premises onto AWS, Azure, and GCP
Education
North American University
M.S. in Computer Software Engineering
M.S. in Cybersecurity
Turkish National Police Academy
Bachelor's degree in Security Sciences (Cybersecurity)
Technical capabilities
Areas of depth
Software supply-chain security · Platform strategy and paved roads · Reliability engineering (SLOs, rollback, MTTR) · Multi-cloud migration · AI/ML platform
Tools I reach for
Cloud
AWS · Azure · GCP
Kubernetes
EKS · AKS · GKE · OpenShift · Helm · ArgoCD · OPA Gatekeeper
Infrastructure as code
Terraform · OpenTofu · CloudFormation · Ansible
Delivery & supply chain
GitHub Actions · Jenkins · Harness · CodePipeline/CodeBuild · Nexus Repository, IQ, and Firewall · Checkmarx One · SonarQube · SBOM
Observability
Prometheus · Grafana · Datadog · Dynatrace · Splunk
AI/ML platform
MLflow · model registries · MCP · LangGraph
Languages
Python · Bash · HCL · SQL
Local workstation
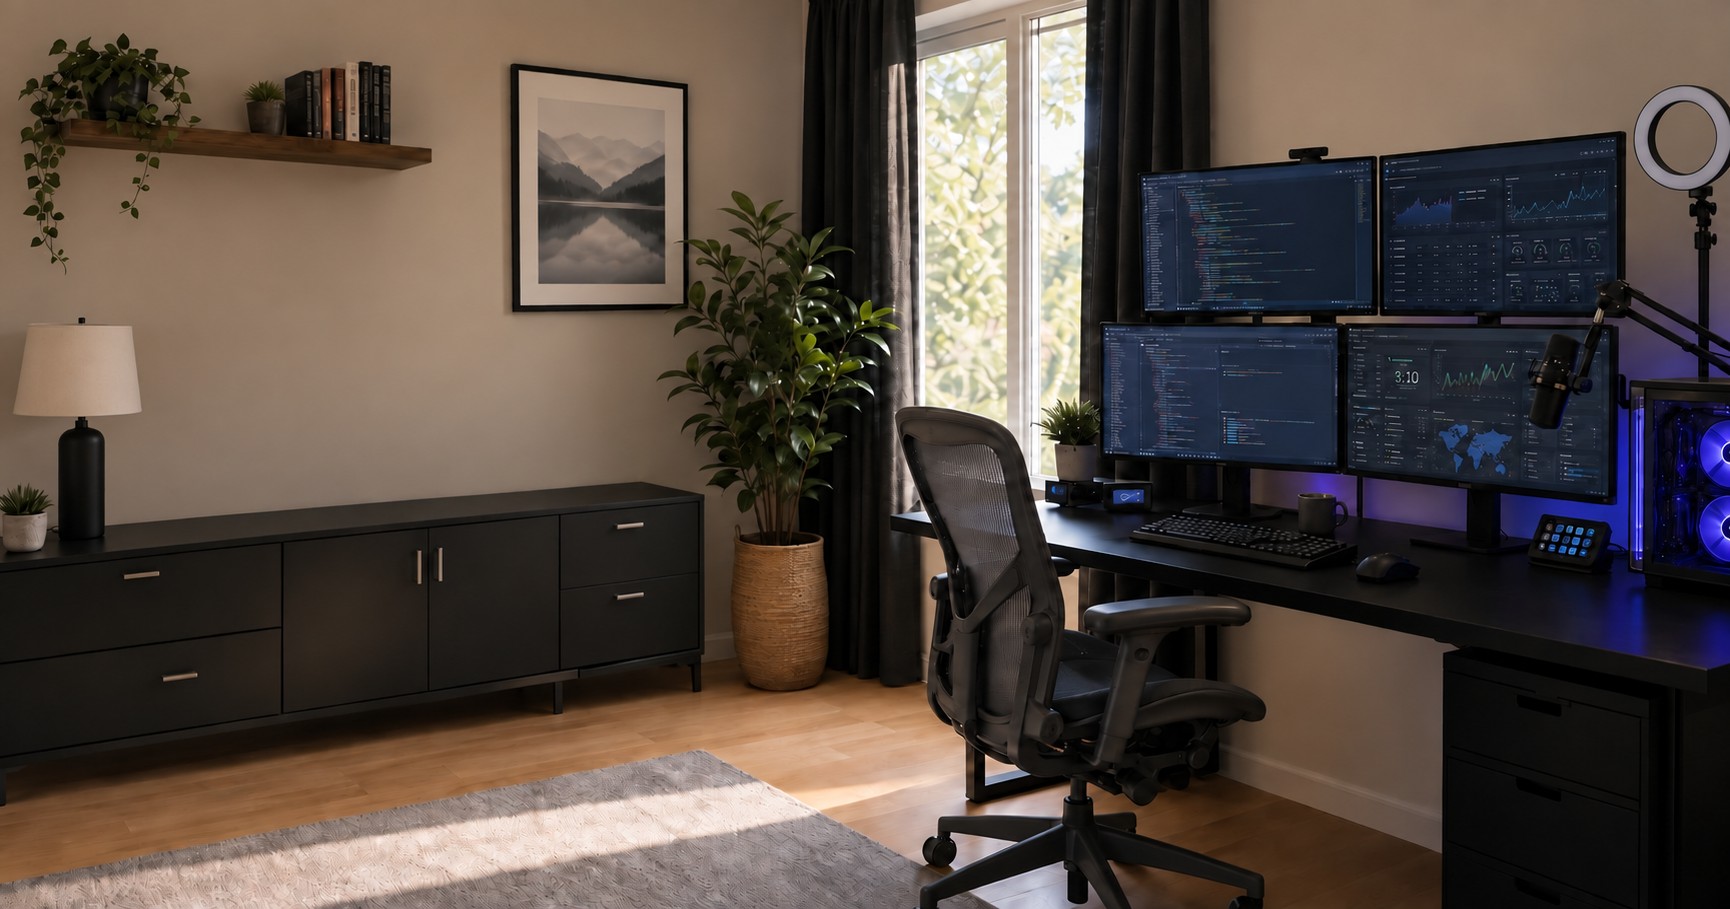
The local lab where AI tooling gets tested before it reaches a team. The glass PC in the room is this dual-GPU workstation.
- Processor: AMD Ryzen 9 5900XT (16 cores / 32 threads)
- Primary GPU: NVIDIA GeForce RTX 3060 (12 GB VRAM)
- Secondary GPU: NVIDIA GeForce RTX 2060 (6 GB VRAM)
- System memory: 32 GB RAM (31.9 GiB addressable)
- Custom build: Fully built by me; parts selected, assembled, and configured
Hardware verified locally on 31 Aug 2026.
Professional experience
Cognizant · Senior DevOps Engineer
Sep 2019 – Present · Remote
- Leadership advisory. Advise senior engineering leadership across architecture, software engineering, and AI/ML on the internal and external tooling their organizations depend on, using real production scenarios to shape solution and implementation decisions. Mentor 30+ engineers on ticket handling and application security.
- Delivery path. Architected the shared delivery path and drove its adoption (Jenkins, CodePipeline/CodeBuild, GitHub Actions, and Harness) with SonarQube and Nexus IQ gates and automated promotion rollback; 50+ microservices ship on it and deployment lead time fell 40%.
- Supply chain. Architected software supply-chain governance for 6,300+ developers: Hugging Face, npm, Maven, and PyPI intake through governed Nexus proxies and Firewall rules, per-application SBOMs, Checkmarx One gates, and automated fix pull requests (Golden PRs).
- Artifact platform migration. Owned the zero-downtime move of the artifact platform behind 7,000+ applications to AWS end to end (parallel blue-green environments, checksum-validated artifacts, rollback held open through cutover) at 99.99% availability; then cut its storage spend 98% with automated S3 versioning and lifecycle tiering.
- Reliability. Established platform SLAs and SLOs with automated canary rollback, and connected ServiceNow ticketing and incident diagnostics through Model Context Protocol (MCP) integrations, reducing MTTR across multi-cluster Kubernetes.
- Multi-cloud. Led the move of 20+ applications from on-premises to AWS, Azure, and GCP onto one Kubernetes release model (EKS, GKE, and AKS with Helm, ArgoCD, RBAC, and network policy) on standard network baselines and Terraform/CloudFormation infrastructure.
- Release promotion. Replaced manual UDeploy release steps with compliant multi-environment promotion, artifact lineage, and rollback points.
- AI/ML platform. Brought model workloads onto the platform: governed Hugging Face intake and MLflow/ECR model-registry workflows.
- Wall Street financial advisory platform (2019–2022). Modernized data-center infrastructure and release automation for a Wall Street asset-management project running investment and financial advisory systems.
EPAM Systems · Senior DevOps Engineer
Nov 2018 – Sep 2019 · Oil & Gas IoT · Remote
- Supported an Oil & Gas IoT program aggregating subsea pipeline telemetry; deployed its data services on Kubernetes with custom Helm charts and namespace isolation.
- Provisioned environments with Terraform and Ansible and built delivery pipelines and alerting for data-processing services.
NDA Asset Management · Systems Engineer
Jul 2015 – Nov 2018 · On-site
- Built Terraform modules for AWS, cutting environment setup time 60%, and managed Ansible configuration and patching across 100+ servers.
- Automated Jenkins build, test, and deploy pipelines for same-day releases, eliminating 70% of manual configuration.
INTERPOL · Systems Engineer
Apr 2012 – May 2015 · On-site
- Integrated regional web tools with the I-24/7 global communication system and tuned criminal-intelligence query performance.
- Handled security patching, vulnerability remediation, and RBAC/identity management under INTERPOL IT security standards.
Case studies: measured impact
01 · Zero-downtime Nexus migration
Assessed application dependencies on the Nexus repositories first, then built parallel AWS infrastructure on EC2, S3, and RDS and cut over with a blue-green DNS switch. Artifact integrity was checksum-validated across environments and rollback stayed available through the live traffic switch: 99.99% availability, no migration downtime. Automated S3 versioning and lifecycle tiering cut Nexus repository cloud-storage spend by 98%; the platform now supports 7,000+ dependent applications.
02 · A paved road for 50+ services
Mapped how 50+ services actually reached production, then replaced the per-team paths with reusable CodePipeline and CodeBuild templates carrying SonarQube and Nexus IQ gates and promotion gates with automated rollback. Lead time fell 40%, and every service now clears the same checks.
03 · Multi-cloud migration factory
Classified workloads by cloud suitability (cost, latency, compliance) before moving any of them, then migrated 20+ applications from on-premises to AWS, Azure, and GCP on reusable Terraform modules per provider. ArgoCD GitOps workflows handle multi-cluster delivery; network peering, VPN, and security group configurations were validated per environment.
04 · One operating model for four Kubernetes estates
Standardized cluster bootstrap with eksctl, gcloud, and az CLI automation, built a unified Helm chart library for microservice deployments, and drove multi-cluster GitOps with ArgoCD ApplicationSets across EKS, GKE, AKS, and on-premises OpenShift. Prometheus + Grafana federation covers cross-cluster observability; network policies, RBAC, and OPA Gatekeeper are enforced on every cluster.
Selected builds
The same idea outside work: stop unsafe changes before they land.
Agent Orchestration TUI (private build)
Human-in-the-loop cockpit for AI coding agents: Claude plans, Codex/OpenAI writes, DeepSeek reviews, and nothing touches the repo until a human approves the patch. Repo-aware runs with live streaming and durable SQLite history.
Python · Textual · LangGraph · SQLite · Langfuse
ReadThePlan (public MIT release v0.4.0)
A guardrail for infrastructure changes: classifies every Terraform/OpenTofu plan as safe, review, dangerous, or irreversible before apply. Shipped as a CLI and GitHub Action with documentation and a browser playground.
github.com/readtheplan/readtheplan
Production delivery
The paved road every service ships on: how a change travels from a merge to running in production, and what is allowed to stop it on the way.
Stages
- Source: a merge to the service repository triggers CodePipeline.
- Build: CodeBuild compiles and pushes the image to ECR.
- Quality gate: SonarQube fails the run on quality regressions.
- Dependency gate: Nexus IQ scans the artifact against Nexus Repository policy before promotion.
- Delivery: ArgoCD syncs the chart out to the EKS clusters.
Operating rules
- Environment promotion gates carry automated rollback; one reusable template covers 50+ microservices
- Artifact integrity is checksum-validated across environments
- Helm, RBAC, and network policies are standardised across EKS, GKE, AKS, and on-premises clusters
- Release promotion is tracked end to end, with artifact lineage and rollback points per environment
Platform fleet
EC2 · S3 · RDS · Redshift · Lambda · EBS · ELB · Auto Scaling · SNS · CloudFormation, with Splunk Universal Forwarder standardised across Linux and Windows fleets.
Decisions
Architecture decision records for the platform work: what was decided, what it cost, and what it changed.
ADR 001 Cut Nexus over blue-green, not in place
- Context
- Nexus Repository and Nexus IQ sit in the build path of 7,000+ dependent applications. Moving them to AWS could not break builds or strand artifacts.
- Decision
- Stand up parallel AWS infrastructure on EC2, S3, and RDS, checksum-validate every artifact across environments, then switch traffic with a blue-green DNS cutover while the old environment stays live for rollback.
- Alternatives
- An in-place migration inside a maintenance window, or moving repositories one at a time behind mixed routing.
- Tradeoff accepted
- Two full environments run in parallel for the migration window. That cost buys an instant, rehearsed rollback path.
- Outcome
- Zero-downtime cutover with 99.99% availability maintained. Automated S3 versioning and lifecycle tiering then cut Nexus cloud-storage spend by 98%.
ADR 002 Route every public package and model through one governed proxy
- Context
- A platform team serving 6,300+ developers pulls from Hugging Face, npm, Maven, and PyPI. Each direct download is an unreviewed supply-chain entry point.
- Decision
- Serve all four ecosystems through Nexus proxies, with Nexus Firewall controlling what is ingested and Nexus IQ producing SBOM reports for what is consumed.
- Alternatives
- Let builds reach the internet and scan afterwards, or maintain allowlists team by team.
- Tradeoff accepted
- The proxy becomes critical shared infrastructure on every build path, which is why its migration was designed around rollback (ADR 001).
- Outcome
- Dependency and model intake is governed at one point, and each application has an SBOM instead of an unknown dependency tree.
ADR 003 Ship vulnerability fixes as pull requests, not tickets
- Context
- Nexus IQ and Checkmarx One surface vulnerable dependencies faster than owning teams can research and patch them.
- Decision
- Generate automated vulnerability-fix pull requests (Golden PRs) and enforce Checkmarx One gates in source control.
- Alternatives
- File findings as tickets for each owning team to investigate.
- Tradeoff accepted
- The platform team owns the fix automation and has to keep the pull requests it opens small, correct, and mergeable.
- Outcome
- Remediation arrives as a reviewable diff inside the normal delivery flow instead of as a backlog item.
ADR 004 One delivery template with gates, not a pipeline per team
- Context
- 50+ microservices each carried their own path to production, with inconsistent quality and dependency checks.
- Decision
- Provide reusable CodePipeline/CodeBuild templates, alongside Jenkins, GitHub Actions, and Harness workflows, with SonarQube and Nexus IQ gates and environment promotion gates with automated rollback.
- Alternatives
- Keep bespoke pipelines and publish a checklist.
- Tradeoff accepted
- A change to the template reaches every service at once, so the template is changed with the same care as production.
- Outcome
- Deployment lead time fell 40% across 50+ microservices, with the same gates in front of every service.
Open-Source Work
I fix the failure modes that only show up under load (race conditions, resource leaks, and silent diagnostics) in infrastructure other teams depend on.
Selected merged contributions, with the problem each fix addresses. Verified 11 Sep 2026 against GitHub.
-
vLLM Semantic Router
WebSocket concurrency safety. Prevent send-after-close races in room collaboration while preserving non-blocking fan-out and SSE delivery.
vllm-project/semantic-router #3253 · Merged 1 Sep 2026.
-
Hermes Agent
Protecting conversation transcripts. Make timed-out gateway turns fail closed instead of bypassing session locks and writing concurrently to transcripts.
NousResearch/hermes-agent #81029 · Merged 7 Aug 2026.
Authorship preserved: three commits authored by texasich were merged through this pull request.
-
HashiCorp go-plugin
Preventing resource exhaustion. Release Linux process handles during plugin health checks, fixing a file-descriptor leak that grows with plugin count and uptime.
hashicorp/go-plugin #378 · Merged 29 Apr 2026.
-
OpenTofu
Consistent infrastructure diagnostics. Route OpenTelemetry SDK logs through TF_LOG so tracing diagnostics follow OpenTofu’s configured logging.
opentofu/opentofu #4285 · Merged 9 Jul 2026.
More merged work
ReadThePlan (public MIT release v0.4.0)
A guardrail for infrastructure changes: classifies every Terraform/OpenTofu plan as safe, review, dangerous, or irreversible before apply. Shipped as a CLI and GitHub Action with documentation and a browser playground.
github.com/readtheplan/readtheplan
Recent activity & open pull requests
Recent merges
- JustVugg/colibri #1433: Restore the missing build recipe for the shared-batch benchmark. Merged 11 Sep 2026.
- JustVugg/colibri #1432: Replace duplicated Windows environment helpers in tests with the shared compatibility layer. Merged 11 Sep 2026.
- vllm-project/semantic-router #3119: Align the README, development guide, and installer examples with the current Quickstart. Merged 31 Aug 2026.
Open pull requests
Submitted upstream; not merged as of 11 Sep 2026.
- OWASP/MCP-Taxonomy #2: Clarify MCP roots security semantics and deprecation guidance. Opened 7 Sept 2026.
- omacom/omarchy #10557: Add regression coverage for default-no confirmation before Hermes data removal. Opened 6 Sept 2026.
- prowler-cloud/prowler #12733: Add Microsoft 365 mappings for Cyber Essentials 3.3 using existing checks. Opened 3 Sept 2026.
Additional work and current activity: github.com/texasich
Certifications
- AWS Certified Solutions Architect (Professional)
- AWS Certified SysOps Administrator (Associate)
- CompTIA Security+ (SY0-701)
Cloud architecture, AWS operations, and security fundamentals: the current credentials behind the Terraform, Kubernetes, and patch-compliance work above.